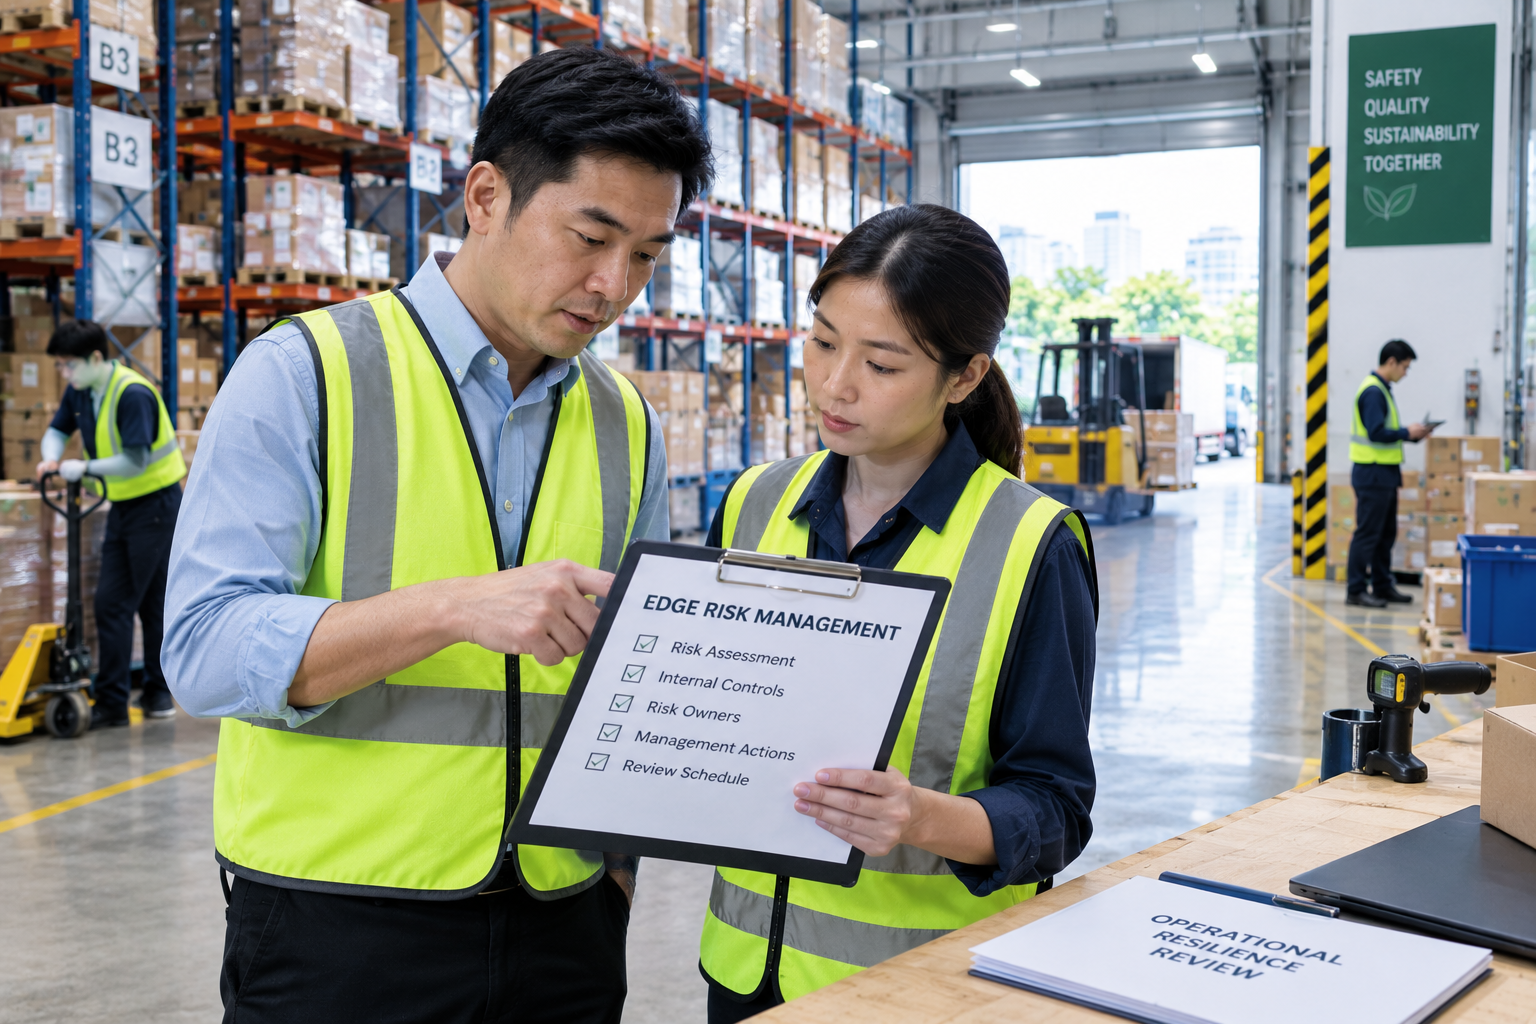
Many Singapore SMEs operate successfully for years with relatively informal management structures.
The founder approves major payments.
Department heads manage their own processes.
Financial reporting is reviewed periodically.
Operational problems are resolved through direct communication.
This approach may be workable when the organisation is small.
However, as the company grows, the same informal arrangements can create vulnerabilities.
More employees, larger transaction volumes, additional suppliers, new business locations and increasingly complex operations introduce risks that management may not be able to monitor through personal oversight alone.
This is where EDGE Enterprise Risk Management and Internal Controls becomes relevant.
EnterpriseSG provides support for initiatives involving risk assessments, internal controls development and risk governance frameworks to support long-term business stability and growth.

Enterprise Singapore
+1
The objective is not to eliminate every business risk.
It is to help management identify material exposures, establish accountability and implement appropriate controls before weaknesses become costly operational problems.
EDGE Enterprise Risk Management and Internal Controls is a financial management activity under Singapore's EDGE Grant.
It supports eligible businesses in developing structured approaches to identifying, assessing and managing enterprise risks.
The activity can cover:
EnterpriseSG identifies the following headline support levels:
Business category
Support
SMEs
Up to 50%
Non-SMEs
Up to 30%
The application outcome is indicated as 10 weeks, and the project must be completed within 12 months from approval. Support counts towards the company's overall S$100,000 annual EDGE grant cap.
Enterprise Singapore
These are published programme conditions, not a guarantee of approval or a fixed grant amount.
Risk management is often associated with large corporations, financial institutions or regulated industries.
However, smaller businesses can also experience material losses from weak controls.
Consider a growing distribution company.
Its purchasing activity increases significantly.
Several employees can now approve supplier orders.
Supplier records are maintained across different spreadsheets.
Payment approvals are handled through informal messaging.
No individual has a consolidated view of purchasing exceptions.
The problem is not necessarily misconduct.
It is that the organisation has grown beyond the control structure originally designed for it.
An enterprise risk assessment can help management identify these weaknesses and determine which controls need to be introduced.
A common misconception is that stronger controls automatically mean more paperwork.
In reality, well-designed internal controls should make business processes more reliable.
For example:
The purpose is not to slow the company down.
It is to allow the company to operate with greater confidence as complexity increases.
An audit identifies issues within a defined review scope.
Enterprise risk management takes a wider view of uncertainties that may affect the company's objectives.
It considers not only existing weaknesses but also emerging threats and business dependencies.
A risk register may identify dozens of potential risks.
But if no one is responsible for monitoring them, the document becomes administrative rather than operational.
A control framework must reflect actual business processes.
Overly complicated procedures may create workarounds instead of stronger discipline.
Financial controls are important, but business risks may also arise from operations, technology, suppliers, people and strategic decisions.
A report identifies and recommends.
Management must still assign responsibility, implement agreed actions and review whether controls operate effectively.

Financial risks may arise from weak transaction controls, inaccurate reporting or insufficient oversight.
Examples include:
A company should examine whether financial responsibilities are appropriately distributed.
For example, the same employee should not necessarily be responsible for creating a supplier, approving an invoice and releasing payment without appropriate independent checks.
The appropriate control design depends on the company's size, resources and exposure.

Operational risks arise when processes fail to deliver expected results.
Examples include:
For a growing SME, operational risk management helps management identify where a process is vulnerable to disruption.
The objective is to establish appropriate preventive and corrective controls.

Digital operations introduce additional risks.
These may include:
Risk management should consider how technology-related exposures affect business continuity and information integrity.
This is distinct from purchasing cybersecurity software.
The focus is on understanding risks, establishing controls and defining management responsibilities.
As companies grow, responsibilities often become more distributed.
Potential exposures include:
A business may discover that several important processes depend on one experienced employee.
The risk is not limited to employee departure.
It also affects business continuity during leave, illness or unexpected disruption.

Strategic risks may emerge from business decisions and external dependencies.
Examples include:
Risk management helps management assess whether significant decisions are supported by adequate information and appropriate oversight.
This is an important distinction.
The EDGE activity is not simply about discussing risks with a consultant.
EnterpriseSG identifies specific project deliverables, including:
Enterprise Singapore
Each deliverable should serve a practical management purpose.
The report should contain:
The report should help management understand where the company is exposed and what improvements are required.
Example format for management discussion, not an official EnterpriseSG template.
Risk ID
OPS-01
Risk
Inventory discrepancies
Risk Owner
Operations Manager
Existing Control
Periodic stock reconciliation
Action
Introduce documented exception review
Review Frequency
Monthly
The purpose of a reporting template is consistency.
Management should be able to compare risk information across departments and identify matters requiring attention.
The manuals provide a reference for how the company manages risk.
They may establish:
The manual should reflect how the business actually operates.
Control self-assessment questionnaires help employees or department heads evaluate whether important controls are present and functioning as intended.
For example:
These questionnaires support recurring management review.
A practical project should progress from understanding the business to establishing usable control frameworks.
Phase 1
Business Risk Assessment
Understand operations, objectives, key dependencies and current risk exposures.
Phase 2
Control Gap Identification
Review existing processes, responsibilities and control weaknesses.
Phase 3
Framework Development
Establish risk ownership, control principles, reporting and escalation arrangements.
Phase 4
Documentation and Management Tools
Prepare the risk report, manuals, reporting templates and self-assessment questionnaires.
Phase 5
Management Adoption
Assign risk owners, communicate responsibilities and establish a review cycle.
EnterpriseSG identifies the following application information for this activity:
Enterprise Singapore
Requirement
Purpose
Vendor proposal
Define the proposed project scope
Vendor quotation
Establish project cost
SS 680 certification
Required vendor-related documentation
One-year revenue growth projection
Explain expected commercial impact
Employment projections
Document anticipated job creation
The employment projections cover overall and Singaporean jobs with gross monthly salary above S$5,000 for one year after project completion.
Businesses should verify the current official requirements before submission.
The Enterprise Risk Management and Internal Controls activity identifies the vendor's SS 680 certification among its application requirements.
Enterprise Singapore
This should be checked during vendor selection rather than left until the application is being finalised.
Management should confirm that the proposed vendor and supporting documents meet the applicable requirements.
A vendor may have broad business consulting experience without necessarily satisfying the specific requirements of this activity.
Compliance and risk management are related, but they are not identical.
Compliance focuses on meeting applicable laws, regulations, contractual obligations and prescribed requirements.
Enterprise risk management considers the broader uncertainties that could affect the company's objectives.
For example:
A company may comply with its accounting obligations while still having weak management reporting.
It may satisfy employment requirements while remaining highly dependent on one critical employee.
It may have standard operating procedures but lack a structured process for identifying operational disruptions.
The EDGE activity focuses on risk management initiatives and internal controls.
EnterpriseSG specifically lists regulatory compliance and updates to Standard Operating Procedures among non-supported costs for this activity.
Enterprise Singapore
Businesses should therefore distinguish genuine risk framework development from routine compliance or procedural updates.
A company can possess a detailed risk register and still have weak risk management.
The problem often lies in ownership.
Consider the following illustrative allocation:
Risk area
Suggested management owner
Financial reporting
Finance lead
Supplier concentration
Procurement or operations lead
Inventory control
Operations manager
Technology access
IT or designated system owner
Business continuity
Management sponsor
Strategic investment
Senior management
The exact allocation depends on the organisation.
What matters is that each material risk has an accountable owner who understands:
This turns risk management into a management responsibility rather than a consultant-owned document.
Growth introduces new operating conditions.
A company opening a second location may need stronger reporting and financial controls.
A business entering a new market may face unfamiliar commercial and supplier dependencies.
A manufacturer increasing production volume may need more reliable quality and inventory controls.
A company adopting new systems may need clearer access and information management procedures.
Risk management helps management identify these changes before they become major disruptions.
The objective is not to prevent expansion.
It is to ensure that organisational controls develop alongside business complexity.
EnterpriseSG states that the Enterprise Risk Management and Internal Controls project must be completed within 12 months from approval.
Enterprise Singapore
Businesses should therefore establish a realistic scope and implementation schedule.
The project should account for:
A project that requires substantial operational input should not be scheduled as though it were simply a document preparation exercise.
The official activity page states that costs incurred from the date of application are covered upon approval. It also states that the business must not have started work or made payment or deposit to a supplier, vendor or third party before application submission.
Enterprise Singapore
Businesses should therefore distinguish between:
Do not assume that work or expenditure incurred before application submission can be included retrospectively.
EDGE grant support is disbursed on a reimbursement basis.
For this activity, EnterpriseSG states that:
Enterprise Singapore
The published disbursement timelines are:
Payment method
Published timeline after claim approval
PayNow Corporate
14 working days
GIRO
Up to 8 weeks
These timelines apply after claim approval, not from the date of application.
Businesses should plan their working capital accordingly.
Before proceeding, management should confirm:
The company has identified a genuine need for stronger risk management.
Existing risk management practices have been reviewed.
The project covers more than routine compliance updates.
The vendor meets the applicable requirements.
SS 680 certification requirements have been checked.
Project deliverables are clearly defined.
Risk reporting and ownership arrangements are included.
Management action points can be implemented.
Revenue and employment projections are prepared.
The project can be completed within the approved period.
Cash flow is sufficient for reimbursement-based funding.
No prohibited pre-application work or payments have occurred.
Avoid:
The purpose is to develop a practical system that management can continue using after the consulting engagement ends.
A business becomes more mature when it can operate reliably without depending entirely on the founder's personal oversight.
This requires more than adding employees or introducing technology.
It requires clear responsibilities, consistent processes, management visibility and structured decision-making.
EDGE Enterprise Risk Management and Internal Controls provides a potential pathway for eligible companies to strengthen these foundations.
For Singapore SMEs preparing for expansion, the strategic objective is straightforward:
Build a business that can grow without allowing operational complexity to outpace management control.
If your company is experiencing rapid growth, expanding its operations or seeking to strengthen internal controls, we can help assess the proposed project scope, identify relevant EDGE considerations and structure a practical risk management initiative.
Our focus is on building stronger enterprise capabilities, not producing documentation that remains unused.
Book a 30-minute, no-obligation discussion here:
 WhatsApp us
```